Volkis News

We got phished! (but it was just a test)

We got phished! (but it was just a test)

Posted on 2024-05-17by alexeiin Volkis News


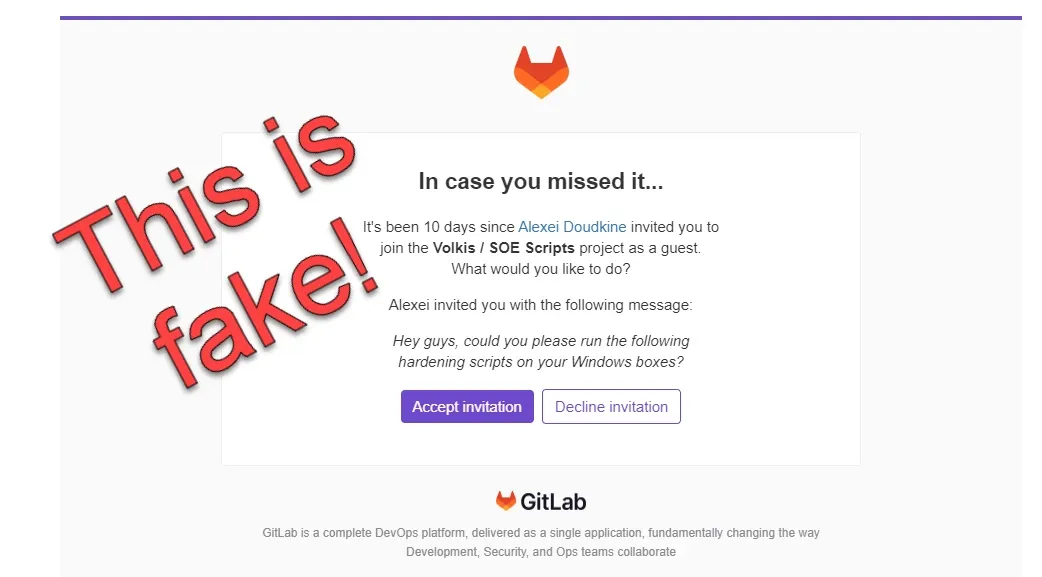
Over the last couple of weeks, we had a fellow security consultancy perform a penetration test on us! That’s right, even though we can do it ourselves, it’s always best to get someone independent to look at your security. We believe in following our own recommendations, so here we are. What did we learn?
Continue reading
Our first growing pains

Our first growing pains

Posted on 2023-03-21by mattin Volkis News


Earlier this year Alexei and I were staring at the screen, looking at a report that was less than flattering for the company. The reading of the report was simple: we were doing less billable work than we expected.

Continue reading
Report Ranger roadmap

Report Ranger roadmap

Posted on 2023-02-23by mattin Volkis News


When we started Volkis, Alexei and I had a big ranty discussion on how reports should be done. The next day I hacked together a PoC. We looked at it and went “damn, we already like this better than what’s already out there!”

Continue reading
We were vulnerable - how a security company could have vulns

We were vulnerable - how a security company could have vulns

Posted on 2022-06-22by alexeiin Volkis News


Well, it finally happened! We received the first submission to our Vulnerability Disclosure Program with actual possible impact. And, although it didn’t actually affect us or our clients in any way, it could have. So we awarded it a P3! But how could this happen? We’re security experts ourselves, so shouldn’t we have picked up on it? Well, as we always tell our clients, “security is hard” and no one is perfect.

Continue reading
The value that Volkis brings as a company for penetration testing

The value that Volkis brings as a company for penetration testing

Posted on 2022-04-13by mattin Volkis News


When building a cyber security company there’s a question we have to keep front of mind at all times. What value do we bring as a company? It’s one thing to just say “yes of course we provide value as a company” but for me I’ve tried to make an actual list. I’ve put up the results of this up in a new handbook page.

Continue reading
State of Volkis - what do we do well and what should we improve?

State of Volkis - what do we do well and what should we improve?

Posted on 2022-02-04by mattin Volkis News


A few weeks ago we had an internal strategy session with everyone at Volkis. In this session we only discussed four questions:

Continue reading
Our first anniversary

Our first anniversary

Posted on 2021-02-09by mattin Volkis News


Today marks the 1 year anniversary of our official launch!

Continue reading
Volkis Stage 2

Volkis Stage 2

Posted on 2021-01-05by alexeiin Volkis News


Last year was definitely… something. I’m glad its over and although we’re not out of the woods yet, I am hopeful that 2021 will bring a much needed peace for us all. That being said, Volkis is now in its 2nd year of operation! Our first year was an amazing ride and such a humbling learning experience; equal parts excitement and terror!

Continue reading
New guides, welcome packs, and methodologies in the Volkis Handbook

New guides, welcome packs, and methodologies in the Volkis Handbook

Posted on 2020-04-07by Volkisin Volkis News


A couple of weeks ago we put up the Volkis Handbook. It is aimed at our customers, friends, employees, infosec colleagues and really anyone interested in the inner workings of Volkis.

Continue reading
Volkis up and running!

Volkis up and running!

Posted on 2020-03-24by Volkisin Volkis News


Since the start we’ve had a remote-first philosophy and even with these troubled times we’re up and running providing penetration testing, security consulting, and strategy work. There are obviously a few things we can’t do for now such as internal penetration testing, physical intrusion, and onsite debriefs, but most of our services including external and web app penetration testing, red team, security strategy, and compliance are still running.

Continue reading